
DOH Mandates It. Breaches Destroy Reputations.
ADHICS Compliance, Secure Health Data or Face Enforcement
Every healthcare entity in Abu Dhabi must comply with ADHICS cybersecurity standards. The Department of Health enforces through audits, penalties, and license actions. Achieve compliance faster with healthcare cybersecurity automation.
Achieve ADHICS Compliance Fast
Protect health information and secure systems
ADHICS protects Abu Dhabi's healthcare ecosystem.
The Abu Dhabi Health Information and Cyber Security Standard is DOH's cybersecurity framework for healthcare. ADHICS applies to every healthcare entity in Abu Dhabi, hospitals, clinics, pharmacies, laboratories, and healthcare IT vendors. The standard covers governance, risk management, asset management, access control, data protection, incident response, and business continuity. DOH enforces ADHICS through mandatory assessments, regular audits, and penalties for non-compliance. Healthcare breaches damage patient trust and trigger immediate enforcement actions. Organizations treating ADHICS as optional IT guidance discover DOH views cybersecurity as fundamental patient safety, and enforces accordingly.
ADHICS is mandatory. Compliance doesn't have to be overwhelming.
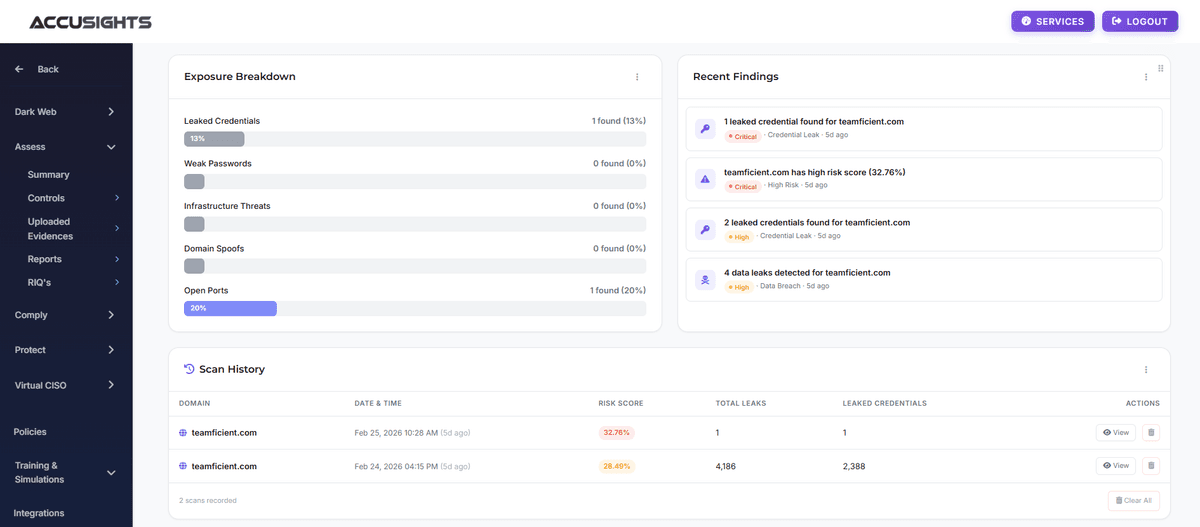
Establish Information Security Governance
ADHICS requires formal information security governance: policies, procedures, roles, responsibilities, and oversight structures. Many healthcare facilities lack basic governance frameworks. Governance failures leave organizations unable to manage cybersecurity risks systematically. Our platform implements ADHICS governance requirements, defines roles, generates policies, and maintains the governance documentation DOH auditors verify during ADHICS assessments.
Security governance. Policy frameworks. Role definitions.
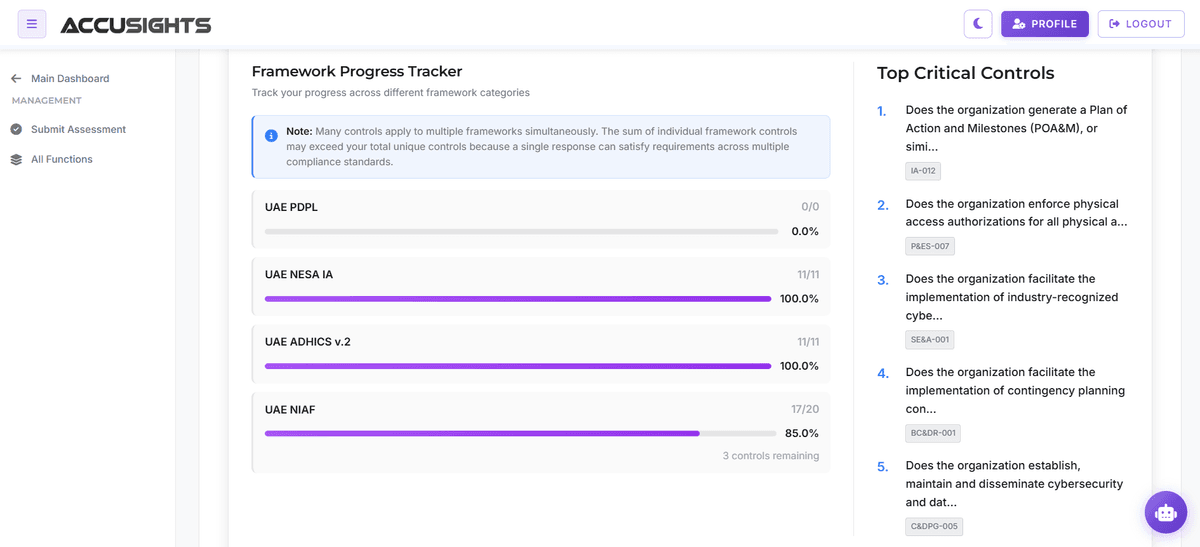
Implement Risk Management and Assessment
ADHICS mandates systematic risk management: asset identification, threat assessment, vulnerability analysis, and risk treatment. Healthcare organizations face sophisticated threats targeting patient data and clinical systems. Risk management failures expose facilities to preventable breaches. Our platform automates risk assessments, identifies vulnerabilities, prioritizes remediation, and maintains the risk registers DOH expects during ADHICS compliance verification.
Risk assessment. Vulnerability analysis. Remediation tracking.
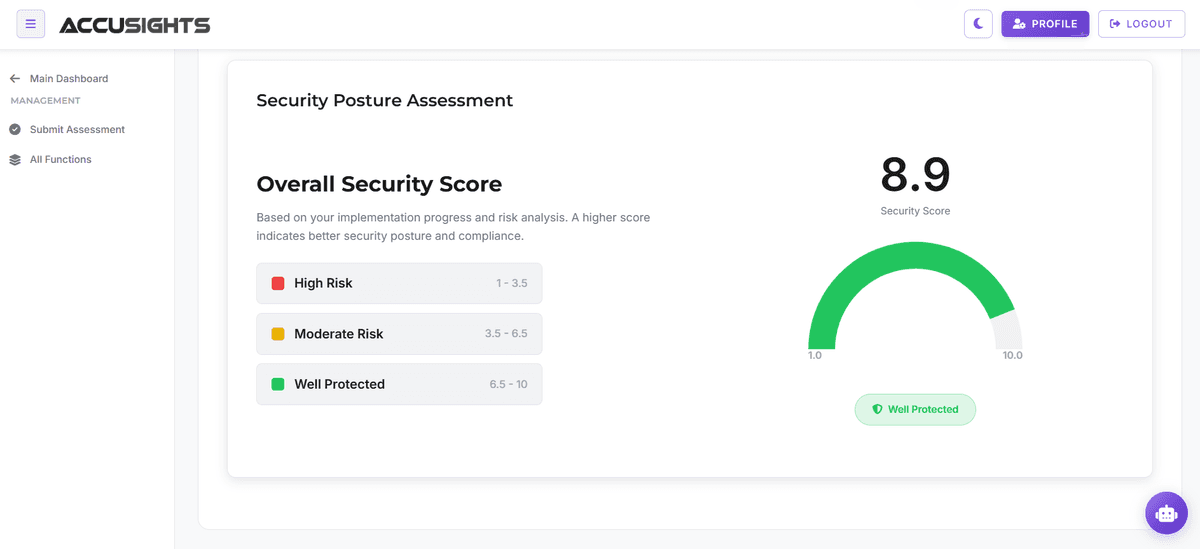
Implement Access Control and Data Protection
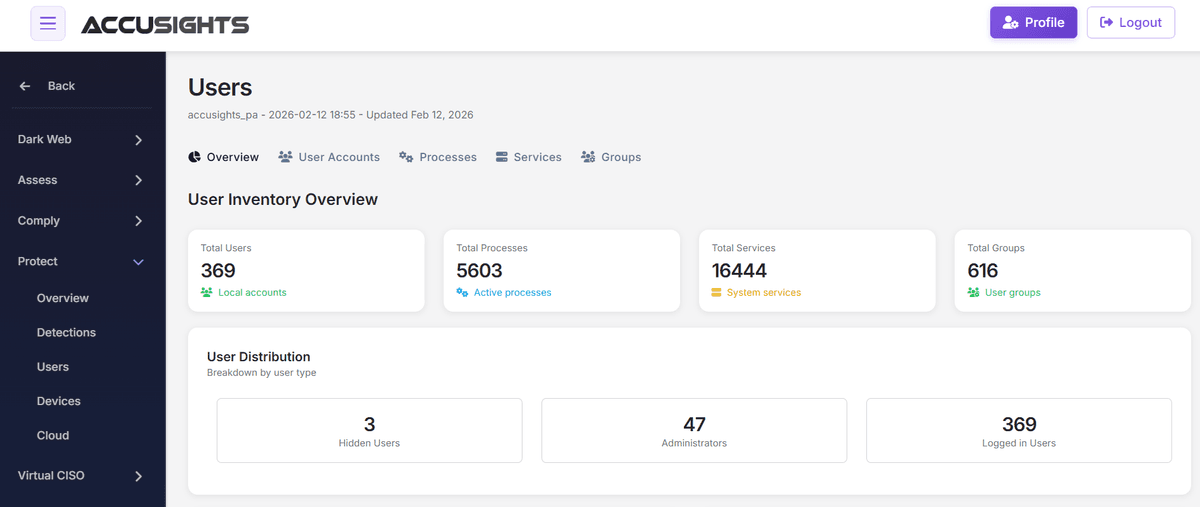
ADHICS requires strict access controls: user authentication, authorization management, privileged access controls, and data encryption. Healthcare data is highly sensitive and attractive to attackers. Access control failures enable insider threats and external breaches. AccuSights maps the ADHICS access-control requirements, validates through read-only telemetry whether multi-factor authentication, privilege assignment and encryption are configured on supported platforms, and keeps the evidence DOH reviews during security audits. The settings themselves are changed by your own administrators.
Access requirements mapped. Settings validated read-only. Evidence kept.
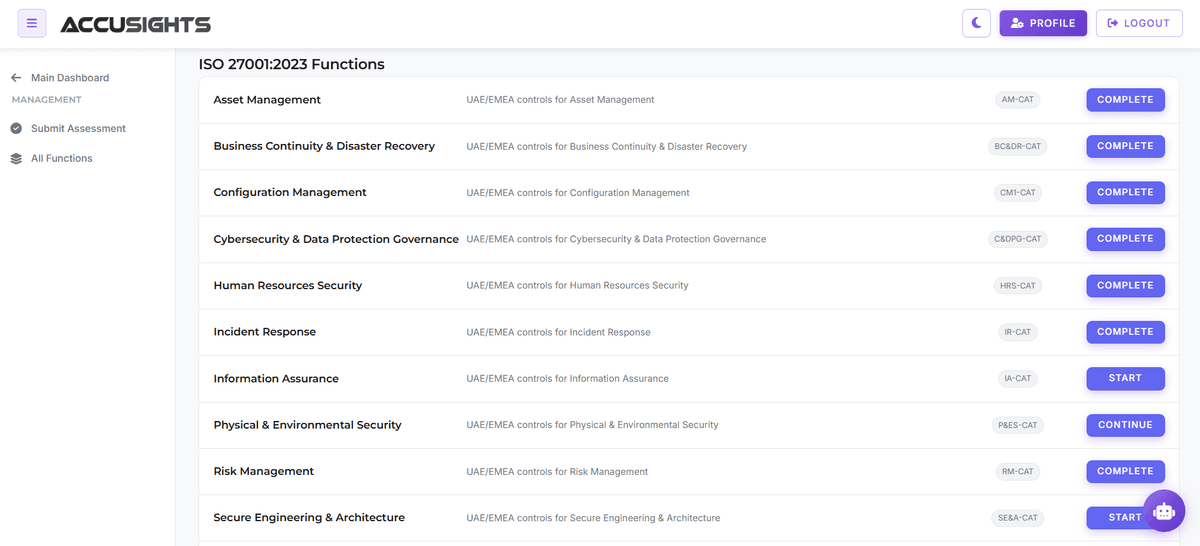
Establish Incident Response and Recovery
ADHICS mandates incident response capabilities: detection, analysis, containment, eradication, recovery, and lessons learned. Healthcare breaches require immediate response to protect patients and comply with notification requirements. Incident response failures compound breach impact. Our platform manages incident response workflows, coordinates activities, documents actions, and maintains the incident records DOH examines during compliance assessments.
Incident detection. Response coordination. Recovery procedures.
Maintain Business Continuity and Disaster Recovery
ADHICS requires business continuity planning: impact analysis, recovery strategies, backup procedures, and testing. Healthcare cannot tolerate extended downtime, patient care depends on system availability. Continuity failures threaten patient safety and violate DOH requirements. Our platform implements continuity planning, manages backups, schedules testing, and maintains the continuity documentation DOH requires for ADHICS compliance.
Continuity planning. Backup procedures. Recovery testing.
Prepare for DOH ADHICS Audits
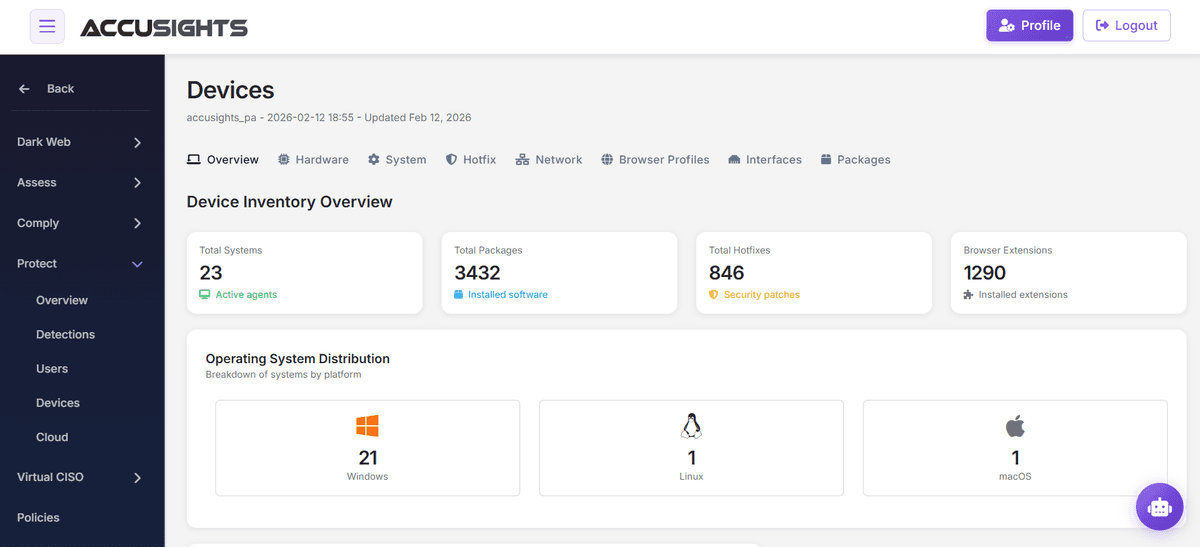
DOH conducts regular ADHICS compliance audits examining the domains and controls that apply to your entity type and tier, out of 692 controls across 11 domains. Audits assess governance, technical controls, documentation, and evidence of implementation. ADHICS audit failures trigger remediation requirements and enforcement actions. We keep the mapping, the assessment and the evidence in one place, so a DOH audit becomes a file hand-over rather than a scramble.
Evidence kept current. Complete documentation. Systematic compliance.
Why Healthcare Entities Choose This Path
From cybersecurity gaps to ADHICS compliance.
Healthcare facilities using our platform:
Walk Into DOH Audits Ready
Requirements mapped, implementation assessed and evidence in one place, so a DOH ADHICS audit becomes a file hand-over rather than a scramble.
Protect Patient Data
ADHICS controls protect health information from breaches, safeguarding patient trust and avoiding breach notification obligations.
Implement Governance
Formal governance frameworks ensure systematic cybersecurity management across entire healthcare organizations.
Manage Cyber Risks
Systematic risk management identifies vulnerabilities, prioritizes remediation, and reduces exposure to healthcare-targeted attacks.
Respond to Incidents
Mature incident response capabilities ensure rapid detection, effective containment, and minimized breach impact.
Maintain Operations
Business continuity planning ensures healthcare services continue despite cybersecurity incidents, protecting patient care.
Built for Abu Dhabi healthcare cybersecurity and ADHICS readiness.
The 11 ADHICS Control Domains
ADHICS v2 contains 692 controls, 162 primary and 530 secondary, across 11 domains. Applicability and implementation expectations vary by entity type and control category. The platform maps ADHICS requirements, assesses implementation, manages evidence and remediation, and validates selected technical controls through supported telemetry.
The standard runs from workforce security and asset management through access, operations, communications, health information, third parties, systems development, incident management and continuity. Which controls apply to you, and to what depth, depends on your entity type and your tier: Basic, Transitional or Advanced. We confirm your tier first, map your existing controls to the domains that apply, and keep the evidence in one place for licence renewal.
11 domains. 692 controls. Mapped, assessed and evidenced.
ADHICS Security Domains
Healthcare cybersecurity across every domain