
The Dubai free zone
DIFC Data Protection Law, in plain terms
Every company operating in the Dubai International Financial Centre must comply with DIFC Data Protection Law. The Commissioner enforces aggressively, penalties are substantial, and non-compliance can end your license. Achieve compliance faster with purpose-built automation.
Achieve DIFC Compliance Fast
Protect your license and reputation
DIFC's Data Protection Law has real teeth, and uses them.
The Dubai International Financial Centre isn't just another free zone. It's a distinct legal jurisdiction with its own complete Data Protection Law, modeled on GDPR but adapted for Dubai's financial services ecosystem. The DIFC Commissioner of Data Protection actively enforces the law through investigations, audits, and penalties that can reach millions of dirhams. Companies that treat DIFC data protection as optional quickly discover it's mandatory, often through enforcement actions that threaten their license to operate.
DIFC data protection is mandatory. Compliance doesn't have to be overwhelming.
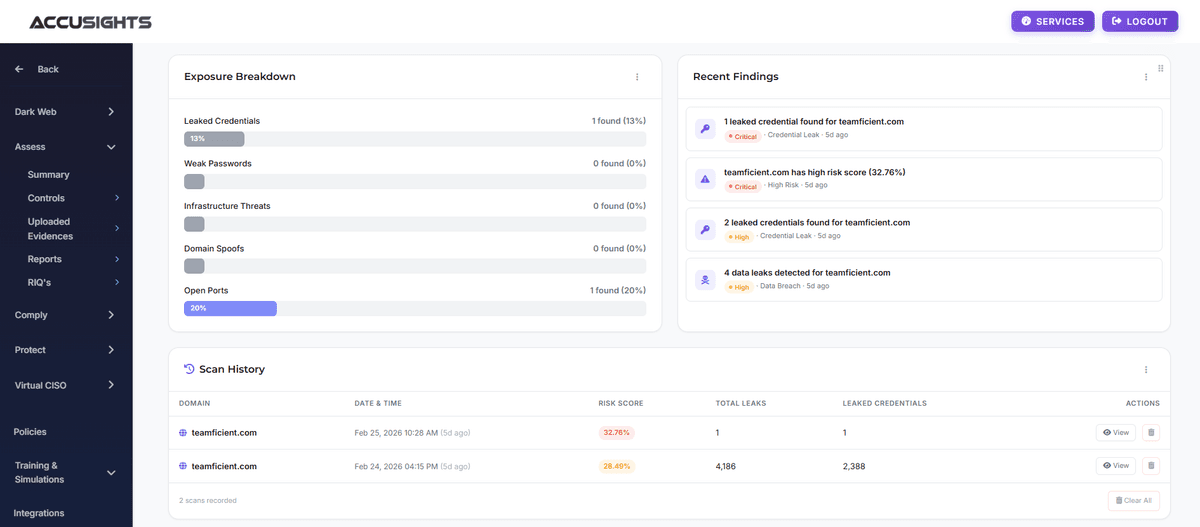
Map Every Data Flow and Processing Activity
DIFC Law requires you to know exactly what personal data you process, where it comes from, where it goes, and why you're processing it. The Commissioner expects complete data mapping during audits. AccuSights structures that work: it records the processing activities you identify, documents the legal basis for each and keeps the Records of Processing Activities (ROPA) in the form the Commissioner expects. Finding the data across your systems is done with your teams, not discovered for you.
Processing activities recorded. Legal bases documented. ROPA kept current.
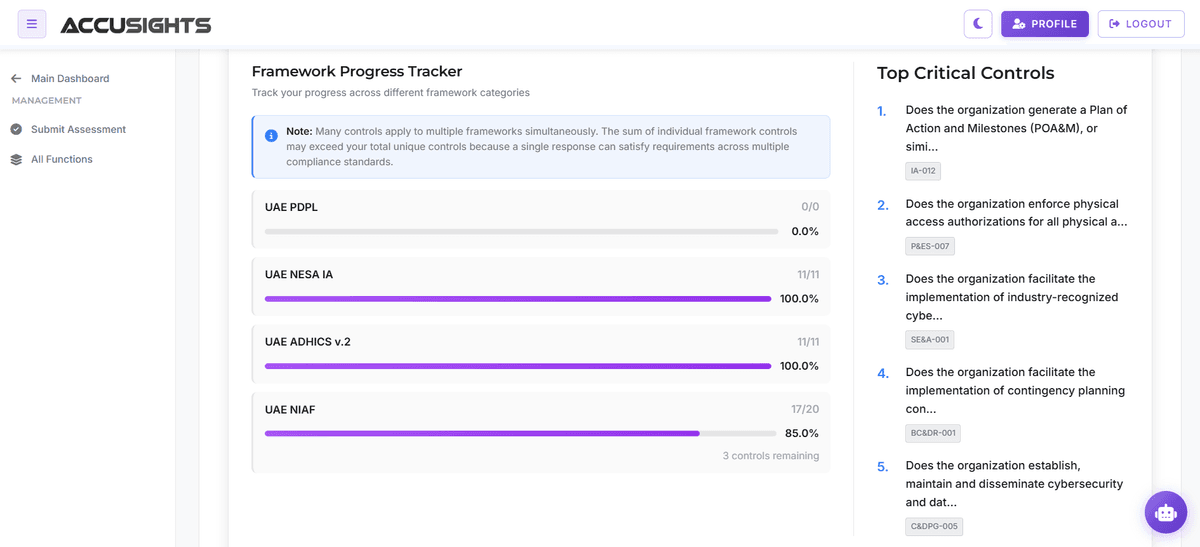
Implement Required Data Protection Controls
DIFC Law mandates specific controls: consent management, data minimization, access controls, encryption, data retention limits, and more. These aren't suggestions, they're legal requirements. Our platform implements controls systematically, documents implementation, and provides evidence the Commissioner expects when investigating compliance.
Systematic implementation. Complete documentation. Audit-ready evidence.
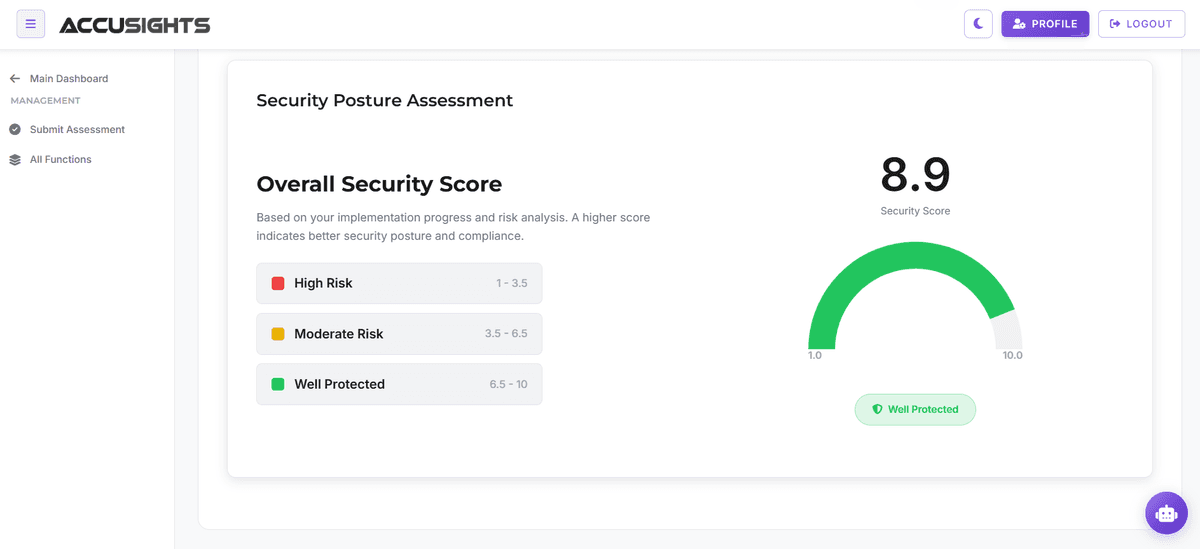
Notify the Commissioner as Soon as Practicable
Article 41 of the DIFC Data Protection Law requires a controller to notify the Commissioner as soon as practicable when a personal-data breach compromises an individual's confidentiality, security or privacy. Notification to affected individuals may also be required where the breach presents a high risk. AccuSights holds the breach-response procedure, records the assessment behind each decision and keeps the notification evidence the Commissioner asks for. Judging the breach and sending the notification stay with the controller.
Article 41 duty mapped. Procedure assessed. Notification evidence kept.
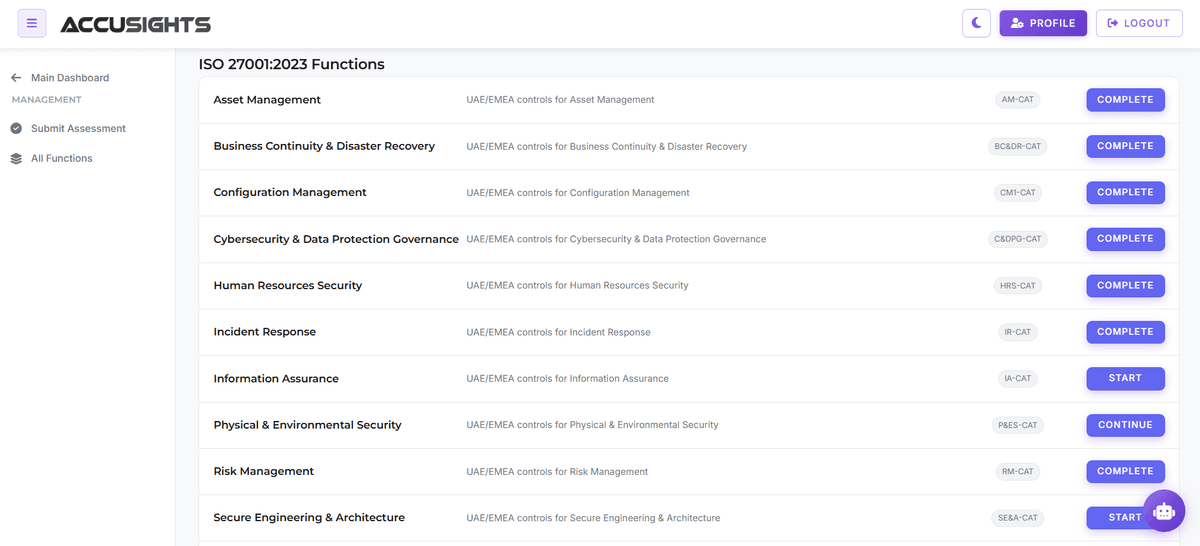
Appoint a Data Protection Officer (If Required)
DIFC Law requires certain organizations to appoint a Data Protection Officer, someone with expertise, independence, and adequate resources. Whether you need a full-time DPO or external DPO services, our platform provides the tools, documentation, and support your DPO needs to fulfill their responsibilities under DIFC Law.
DPO support tools. Compliance documentation. Commissioner liaison ready.
Handle Data Subject Rights Requests Properly
DIFC Law grants data subjects rights to access, rectify, erase, and restrict processing of their data. You must respond within strict timelines. Failures trigger complaints to the Commissioner. AccuSights holds the rights-request procedure, tracks the deadline on each request and keeps the record of what was decided and sent. Verifying the requester and answering them stays with your team.
Procedure documented. Deadlines tracked. Complete audit trails.
Prepare for Commissioner Investigations and Audits
The DIFC Commissioner has broad powers to investigate, audit, and enforce. When they arrive, they expect immediate access to policies, ROPA, breach records, consent documentation, and evidence of controls. Our platform maintains all required documentation in formats the Commissioner expects, turning investigations from existential threats into manageable processes.
Complete documentation. Instant access. Investigation-ready evidence.
Why DIFC Companies Choose This Approach
From compliance anxiety to Commissioner confidence.
Companies using our platform:
Avoid Million-Dirham Penalties
DIFC penalties can exceed AED 1 million. Proper compliance dramatically reduces exposure to enforcement actions and financial penalties.
Protect Your DIFC License
Serious data protection violations can threaten your license to operate in DIFC. Compliance protects your ability to do business.
Pass Commissioner Audits
Complete documentation and implemented controls mean Commissioner investigations become routine audits instead of existential crises.
Meet the Article 41 Notification Duty
A documented breach-response procedure and a kept assessment record mean you can notify the Commissioner as soon as practicable, which is what Article 41 actually requires.
Handle Rights Requests Properly
A documented rights-request procedure and tracked deadlines prevent the complaints to the Commissioner that trigger enforcement actions.
Build Client Trust
DIFC compliance demonstrates commitment to data protection, strengthening relationships with clients who expect the highest standards.
Built for DIFC data protection readiness and continuous compliance management.
Meet Every DIFC Data Protection Requirement
DIFC Law is complete. Our platform covers every requirement.
The DIFC Data Protection Law imposes obligations on controllers and processors, grants rights to data subjects, and empowers the Commissioner to investigate and enforce. Each requirement has specific documentation and implementation expectations. We map the obligations that apply to you, assess whether the policies and controls exist, assign remediation and keep the supporting evidence for Commissioner oversight.
Complete requirements. Systematic compliance. Commissioner-ready documentation.
DIFC Data Protection Requirements
Complete coverage for Commissioner compliance