Cybersecurity & Compliance · Built for the UAE

Every UAE regulator. One program. Compliance turned into security.

Hundreds of line-item requirements across federal, emirate and free-zone rulebooks, and a threat landscape that changes daily, waste your team on checklists instead of securing your assets. Our cybersecurity, risk management and audit experts work with you to build your custom critical security control framework: one set that carries every security and compliance requirement you actually have. It lives in our secure platform, where telemetry proves each control works and keeps compliance continuous for every control and restriction that matters. Up to 80% less manual work, with a read-only compliance agent keeping the picture current.

Mapped across

  • ADHICS
  • DHA
  • NABIDH
  • DIFC
  • ADGM
  • CBUAE
  • CMA
  • VARA
Led by CRISC and CISA certified practitionersA Dubai mainland company with a US practiceIn conversation with the UAE's cyber leadership at GITEX Global 2025 & 2026
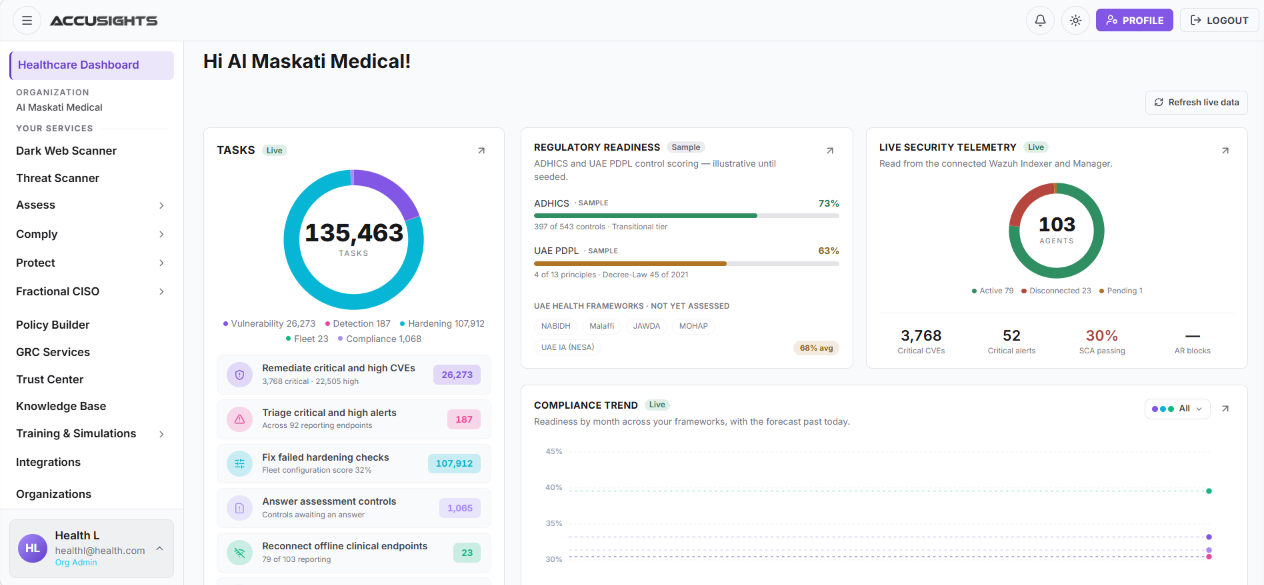
AccuSights healthcare dashboard showing open tasks, ADHICS and UAE PDPL readiness, live security telemetry and compliance trend on one screen

Beyond the UAE

Win bigger contracts,
in any market.

One partner, one control set, and the frameworks that open doors worldwide: SOC 2 for US enterprise deals, ISO 27001 everywhere, GDPR, DORA and NIS2 for Europe, APPI and ISMAP for Japan, cross-mapped to the UAE program you already run. No bench of expensive consultants.

The path of one ADGM payments fintech:

  1. 1

    UAE

    FSRA · CBUAE · PDPL

  2. 2

    United States

    SOC 2 Type II · CMMC Level 2 · HIPAA

  3. 3

    Europe

    GDPR · DORA · NIS2

  4. 4

    Japan

    APPI · ISMAP · JFSA

~600,000

attempted cyberattacks per day were reported during the UAE’s 2026 threat surge

Source: Khaleej Times, April 2026

Tier 1

the UAE's standing in the ITU Global Cybersecurity Index 2024, the top of five tiers

Source: ITU Global Cybersecurity Index 2024

692

controls in Abu Dhabi's healthcare standard alone, before Dubai, Sharjah and federal law

Source: Department of Health Abu Dhabi, ADHICS FAQ

31%

of breaches began with vulnerability exploitation, making it the leading initial-access method in Verizon’s 2026 DBIR

Source: Verizon 2026 DBIR

What simplification means here

One hospital group. Three emirates. Hundreds of requirements. One program.

A hospital with sites in Abu Dhabi, Dubai and Sharjah answers to the Department of Health's ADHICS standard, 692 controls on its own; the Dubai Health Authority's separate rulebook and NABIDH; federal licensing and the Sharjah Health Authority; and the PDPL and the federal health-data law everywhere. Managed as four programs, that is four teams, four calendars and evidence that proves the same thing four ways. Our experts build the group one custom critical security control framework that answers all four rulebooks, host it in the platform, and let telemetry prove every control and keep compliance continuous. Up to 80% less manual work. The regulators get a better answer, and the hours go back to running the hospital.

Abu Dhabi · ADHICS692 controlsDubai · DHA and NABIDHits own rulebookSharjah · federal + SHAlicensing + Law 2 of 2019Federal · PDPLeverywhereYOUR FRAMEWORKexpert-builttelemetry-provenEvery regulator satisfiedEvidence collected onceUp to 80% less manual work

Swipe the diagram to see the whole picture.

34 to 38%higher in-hospital mortality when ransomware hits mid-admission

Peer-reviewed research linking hospital ransomware attacks to patient records found in-hospital mortality rises 34 to 38 percent among patients already admitted when an attack begins, and hospital volume drops 17 to 24 percent in the first week.

The control: Tested, isolated backups that restore in hours; segmented clinical networks; medical-device inventory; and the recovery drill run before it is needed. Care continues because the plan exists.

Source: Neprash, McGlave and Nikpay, American Economic Journal: Economic Policy, February 2026

36additional heart-attack deaths per 10,000 patients a year after a hospital breach

A study of more than 3,000 US hospitals found that after a data breach, time to electrocardiogram slowed by up to 2.7 minutes and 30-day heart-attack mortality rose, as many as 36 extra deaths per 10,000 heart attacks a year, with effects lasting about three years.

The control: Security that clinicians can live with: single sign-on and MFA that add seconds, not minutes; controls designed with the ward, not against it. That is why a physician co-founded this company.

Source: Choi, Johnson and Lehmann, Health Services Research, 2019

59 to 102stroke codes at neighbouring emergency rooms during one hospital's ransomware attack

When a four-hospital system was attacked for a month, the two nearest emergency departments saw stroke activations almost double, waiting times rise by half, and ambulance diversion nearly double. The authors called a hospital cyberattack a regional disaster.

The control: Hospitals are critical infrastructure. Supplier risk management, continuous compliance and continuous proof across the whole chain, to the higher standard the nation expects.

Source: Dameff et al., JAMA Network Open, May 2023

24 hoursfor FSRA-authorised firms to report qualifying cyber incidents

FSRA-authorised firms must report qualifying cyber incidents within 24 hours. DFSA cyber-risk rules have their own notification requirements. Under DIFC Data Protection Law, a qualifying personal-data breach must be reported to the Commissioner as soon as practicable. Each regime wants a rehearsed plan, not a first attempt.

The control: Email data-loss prevention and payment-change verification against fraud; identity protection against account takeover; and an incident procedure rehearsed against every clock that applies to you.

Source: ADGM FSRA Cyber Risk Management Framework; DFSA Cyber Risk Supervision; DIFC Personal Data Breach Reporting

Why the UAE is different

Three layers of rulebooks.
One program.

Federal law, emirate authorities and free-zone regulators each reach your business, and each is serious. Managed separately they multiply work. Mapped once, they become one program on one calendar.

Managing it yourself

Static spreadsheets, one regulator at a time

  • A separate program, audit, and binder for each emirate or zone.
  • The same control documented five different ways, by hand.
  • A point-in-time snapshot that is stale the day after the audit.
  • More manual work, which quietly reduces your actual security.

AccuSights continuous compliance

One mapped control set, always current

  • One control set, cross-mapped to every regulator that applies to you.
  • Evidence collected once and reused across frameworks and emirates.
  • Continuous monitoring, so you are always audit-ready, not cramming.
  • Far less rework, which puts the time back into real security.

The smarter GRC approach in the Middle East is the one that treats your regulators as one program, not five.

How it works

Assess. Comply. Stay ahead, continuously.

Three steps, one platform, and the experts of AccuSights at every one of them. Most firms start with the assessment and never go back to spreadsheets.

  1. Step 1 · Assess

    Know exactly where you stand.

    The assessment maps your assets, your gaps and the regulations that bind you, then hands you a plan ranked by real risk. In plain language, in days.

    • Risk-ranked findings
    • Regulator mapping
    • Plain-language report
    Start with an assessment
  2. Step 2 · Comply

    One control set. Every regulator.

    We cross-map your controls to every framework that applies, collect evidence once, and put renewals on one calendar. Far less rework, permanently.

    • Cross-mapped controls
    • Evidence once
    • One calendar
    See continuous compliance
  3. Step 3 · Continuous

    The agent watches. Issues get fixed fast.

    The read-only agent keeps continuous insight across your infrastructure and cloud. When a control drifts, it surfaces the exact issue with the exact fix, and your team closes it the same day, our engineers guiding.

    • Read-only telemetry
    • Instant insight, guided fixes
    • Always audit-ready
    Meet the Compliance Agent

What we stop

Threats by region, by industry, by the data you hold. And the control that answers each.

Relax about the drift. Every one of these has a known answer, and we keep it running.

~600,000attempted cyberattacks per day were reported during the UAE’s 2026 threat surge

Mohammed Al Kuwaiti, Head of Cyber Security for the UAE Government, said in April 2026 that daily attempts had risen from about 200,000 to about 600,000 since the regional escalation began. The country holds. The question is whether your business would.

The control: The Council’s daily bulletins become checks against your actual assets inside the platform, so national intelligence turns into a to-do list for your engineer.

Source: Khaleej Times, 1 April 2026, quoting the UAE Government's Head of Cyber Security

31%of breaches began with vulnerability exploitation, making it the leading initial-access method in Verizon’s 2026 DBIR

For the first time in the report’s history, exploiting a vulnerability overtook stolen credentials as the most common way in. Every day brings a new one, and only about a quarter of known-exploited flaws get fully fixed.

The control: Patching on a cadence tied to exploited-vulnerability catalogues, with the read-only agent showing which of your systems are exposed today. Relax about the drift; we see it before the attacker does.

Source: Verizon 2026 Data Breach Investigations Report

62%of breaches involve the human element

Phishing, stolen credentials and simple mistakes, with mobile lures now hooking 40% more often than email. In a multilingual workforce the lure comes in whichever language works.

The control: Multi-factor authentication everywhere, email protection, and training in English and Arabic. MFA alone defeats the vast majority of account-takeover attempts.

Source: Verizon 2026 Data Breach Investigations Report

69%of ransomware victims refused to pay last year. They had backups.

Ransomware is present in nearly half of breaches worldwide. The difference between a crisis and a bad day is whether the backups were isolated from the network and tested.

The control: Air-gapped, versioned backups with a restore drill on the calendar. Ransomware becomes a restore, not a negotiation.

Source: Verizon 2026 Data Breach Investigations Report

48%of breaches involve a third party or a leaked credential chain

Client financial data, patient records and contracts leave through email and through the vendors you trust. Third-party involvement in breaches rose 60% in a year.

The control: Email data-loss prevention, encryption for sensitive attachments, vendor access reviews and the critical security controls that apply to your data type, kept effective continuously.

Source: Verizon 2026 Data Breach Investigations Report

45%of employees now use AI at work; 67% through personal accounts

Source code and client data are the most common things pasted into consumer AI tools. Under the PDPL and health-data law, that is a transfer you did not document.

The control: An AI usage policy enforced as a control, approved tools with data-loss prevention, and ISO 42001 alignment when buyers ask. Govern it from the same platform.

Source: Verizon 2026 Data Breach Investigations Report

Open the live UAE threat dashboard →The latest threat headlines →Regional attack data, sector view, and a complimentary threat report.

The reference layer

Bookmark this beside the regulator.

One page per regulator: who is in scope, the current instrument and version, the notification window, the duties in plain language, and a verification date. Free, bilingual, kept current.

The UAE Cyber Security Council, under H.E. Dr. Mohamed Al Kuwaiti, has built one of the most capable national programs anywhere: a National Cybersecurity Strategy for 2025 to 2031, hundreds of thousands of attacks countered every day, daily threat bulletins, national drills that helped financial institutions recover within a day during the 2026 attacks, Cyber Pulse awareness for every resident, and Tier 1 standing in the ITU's global index. Our CEO sat with Dr. Al Kuwaiti at GITEX Global 2025. What we took away was a mandate: the strategy is in place; regulated businesses now need the discipline to meet it without drowning. That is what we bring, with some of the top cybersecurity risk management professionals in the United States and the latest global frameworks, applied to critical infrastructure, hospitals, banks, exchanges and the suppliers they all depend on, to a higher standard of supplier risk management and continuous compliance. UAE Cyber Security Council →

AccuSights is a private company, not a regulator, an auditor or a certifying body. The regulator, auditor or certifying body has the final say on whether you comply. We describe what is published and do not speculate about enforcement. The compliance agent is read-only: it observes and reports, changes nothing, and never accesses a third party's systems without written authorization.

On the calendar

Watch · watching

PDPL Implementing Regulations

Not yet issued as of September 2026, with the Data Office not yet fully operational. The law applies now; the detailed procedures follow. This entry updates the month they are published.

Source: Chambers Data Protection 2026 (March 2026); DLA Piper

Our stance

Real Cybersecurity through efficient and effective Cybersecurity Risk Compliance

A certificate on the wall has never stopped an attack. Compliance done right is a by-product of running securely, and that is the order we work in.

Compliance as paperwork

A binder per regulator, refreshed once a year in a scramble, stale the day after the audit.

The certificate gets renewed while the back door stays open, because nobody is looking between audits.

Tools that hand you a portal and leave your team to drive it, on top of their actual jobs.

The AccuSights order: security first

We help secure your business through continuous compliance, then the same work proves compliance to every regulator that asks.

The read-only agent watches your posture continuously, so between audits is exactly when you are strongest.

GRC experts run the program with you: your obligations, your evidence, your calendar, handled.

Book a demo

See your obligations as one program.

Tell us your sector and we will show you which UAE regulations apply to you, where the gaps are, and how one control set covers them all.

The team replies within one business day, in English or Arabic.