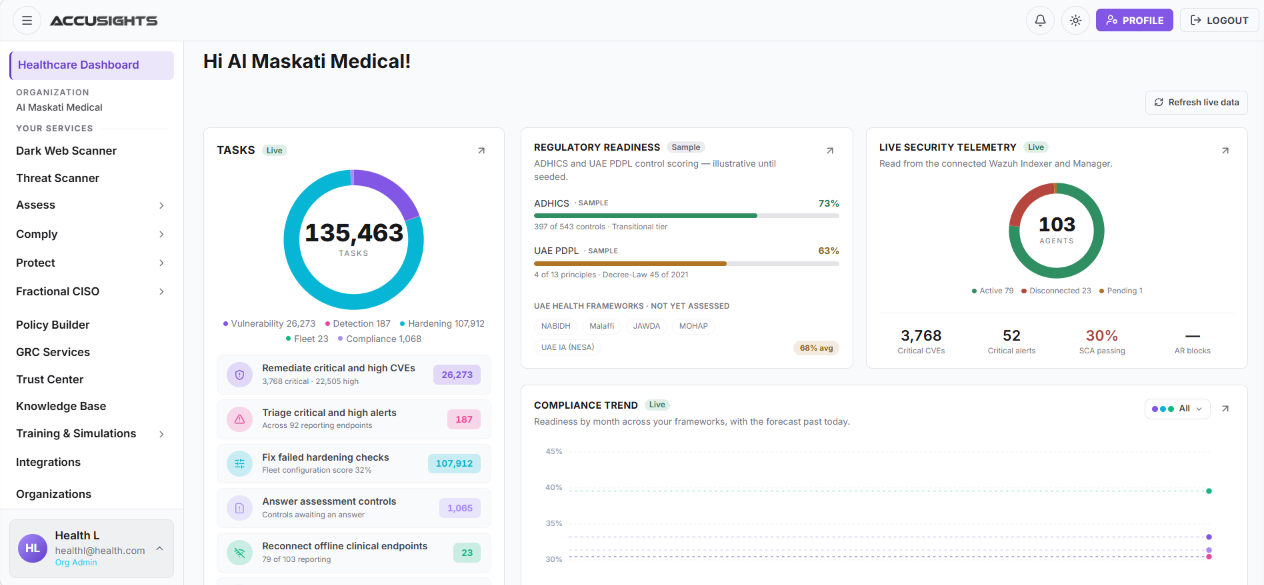
Relax about the drift. Every one of these has a known answer, and we keep it running.
~600,000attempted cyberattacks per day were reported during the UAE’s 2026 threat surge
Mohammed Al Kuwaiti, Head of Cyber Security for the UAE Government, said in April 2026 that daily attempts had risen from about 200,000 to about 600,000 since the regional escalation began. The country holds. The question is whether your business would.
The control: The Council’s daily bulletins become checks against your actual assets inside the platform, so national intelligence turns into a to-do list for your engineer.
Source: Khaleej Times, 1 April 2026, quoting the UAE Government's Head of Cyber Security
31%of breaches began with vulnerability exploitation, making it the leading initial-access method in Verizon’s 2026 DBIR
For the first time in the report’s history, exploiting a vulnerability overtook stolen credentials as the most common way in. Every day brings a new one, and only about a quarter of known-exploited flaws get fully fixed.
The control: Patching on a cadence tied to exploited-vulnerability catalogues, with the read-only agent showing which of your systems are exposed today. Relax about the drift; we see it before the attacker does.
Source: Verizon 2026 Data Breach Investigations Report
62%of breaches involve the human element
Phishing, stolen credentials and simple mistakes, with mobile lures now hooking 40% more often than email. In a multilingual workforce the lure comes in whichever language works.
The control: Multi-factor authentication everywhere, email protection, and training in English and Arabic. MFA alone defeats the vast majority of account-takeover attempts.
Source: Verizon 2026 Data Breach Investigations Report
69%of ransomware victims refused to pay last year. They had backups.
Ransomware is present in nearly half of breaches worldwide. The difference between a crisis and a bad day is whether the backups were isolated from the network and tested.
The control: Air-gapped, versioned backups with a restore drill on the calendar. Ransomware becomes a restore, not a negotiation.
Source: Verizon 2026 Data Breach Investigations Report
48%of breaches involve a third party or a leaked credential chain
Client financial data, patient records and contracts leave through email and through the vendors you trust. Third-party involvement in breaches rose 60% in a year.
The control: Email data-loss prevention, encryption for sensitive attachments, vendor access reviews and the critical security controls that apply to your data type, kept effective continuously.
Source: Verizon 2026 Data Breach Investigations Report
45%of employees now use AI at work; 67% through personal accounts
Source code and client data are the most common things pasted into consumer AI tools. Under the PDPL and health-data law, that is a transfer you did not document.
The control: An AI usage policy enforced as a control, approved tools with data-loss prevention, and ISO 42001 alignment when buyers ask. Govern it from the same platform.
Source: Verizon 2026 Data Breach Investigations Report